
Microsoft is grouping all the options for SQL running in the Azure platform into one portfolio. A family of managed products, making it easier to see them and choose the best for your needs.
Cloud computing requires new security paradigms unfamiliar to many application users, database administrators, and programmers. When it comes to Azure SQL Security, where do you begin?
Azure can be very different from any other data center. While Azure helps secure your business assets, a great deal of responsibility is shared and requires customers to do their part.
In this article, we will see Azure Security best practices. If you are moving toward cloud adoption, you need to be aware of what you need to do to enhance security measures.
Control the database and application access
Centralize the identities management using the Azure Active Directory Authentication (Azure AD):
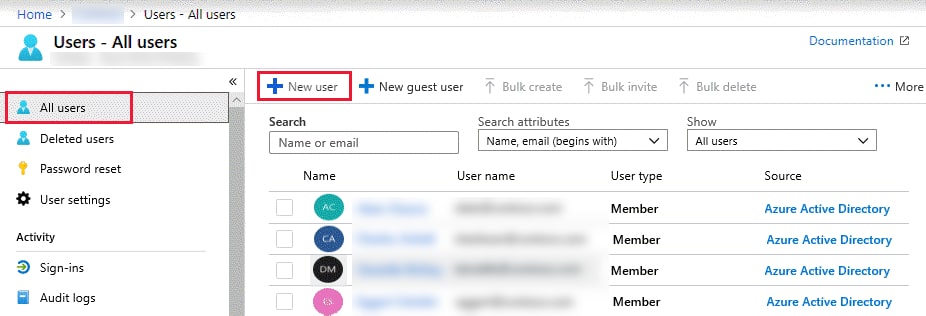
- Create an Azure Active Directory (AD) tenant and create users to represent human users, apps, services, and automation tools.
- In your database, create contained database users that map your Azure AD groups. Put the users associated with your Azure AD groups in database roles with the appropriate permissions.
Grant users the least privileges necessary.
For more details, see the articles: Configure and manage Microsoft Sign-in authentication with Azure SQL and Use Azure AD for authentication with SQL. - Create a separate group for Azure AD administrators for each server or managed instance.
- Monitor Azure AD group membership changes using Azure AD audit activity reports.
For more details, see the article: Audit activity reports in the Azure AD. - Use row-level security and dynamic data masking to limit sensitive data exposure based on users.
Enable Azure multi-factor authentication and minimize the use of password-based authentication
MFA is an authentication method that requires users to ensure through multiple ways that they are who they claim to be.
- Activate Conditional Access in Azure AD (requires Premium subscription).
- Use an Azure AD integrated authentication that eliminates the use of passwords.
- Use cert-based authentication for an application.
- If avoiding passwords or secrets aren't possible, store user passwords and application secrets in Azure Key Vault and manage access through Key Vault access policies.
Protect sensitive data using encryption
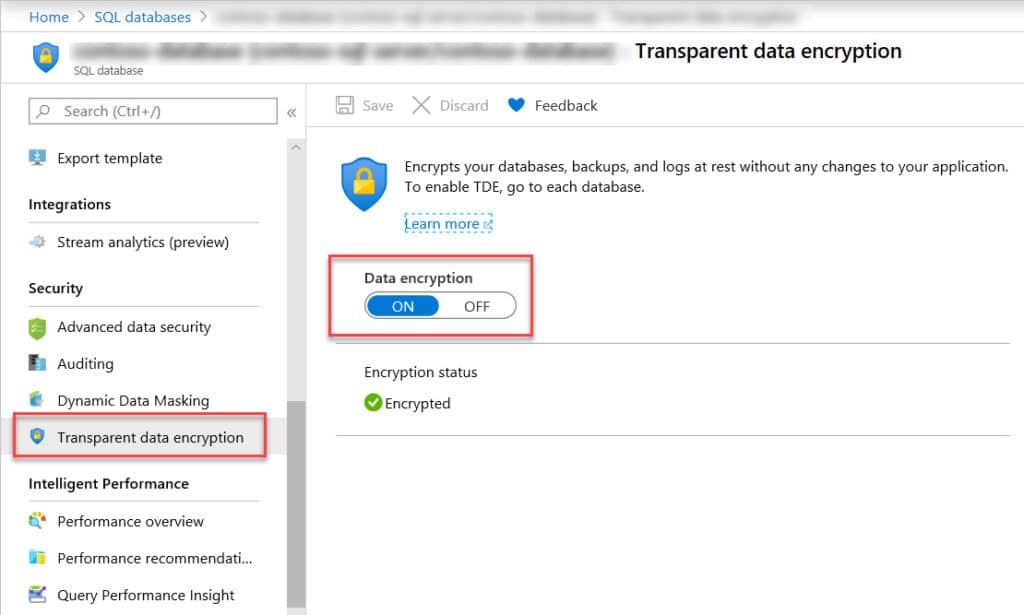
Apply encryption protocols to protect your data between your client and server (in-transit), and when it is persisted in the database, log, and backup files (in-rest).
- If you are in a SQL Managed instance restoring a database from an on-premises server that doesn't have Transparent Database Encryption (TDE) enabled, you will need to allow it manually. Otherwise, TDE is enabled by default for any database created after 2017 in Azure SQL.
- Don't store any data that requires encryption in the master database. This database can not be encrypted with TDE.
- Use Always Encrypted to ensure sensitive data isn't exposed in plaintext, but do not use it as a substitute to encrypt data at rest (TDE) or in transit (SSL/TLS). Microsoft recommends it in conjunction with other security layers.
- Minimize performance and functionality impact using Always encrypted only on sensitive data.
- Ensure that client machines and applications connecting to Azure SQL Database and SQL Managed Instance are using Transport Layer Security (TLS). Prevent clients with well-known vulnerabilities from connecting to Azure SQL (for example, using older TLS protocols and cipher suites).
Implement network access controls
Minimize the number of features that a malicious user can attack, restricting access to Azure SQL Database and SQL Managed Instance.
- Use VNet Service endpoints and VNet Firewall Rules to restrict access to only authorized IP addresses.
- Isolate a SQL Managed Instance inside a virtual network to prevent external access. Use the Network Security Groups (NSG) to restrict access over port 1433 only.
- Use the Private Link feature for a SQL Database. It provides a dedicated private IP for the server inside your virtual network.
Protect databases against attacks

To ensure your databases' security, enable tools to detect and respond to threats as quickly as possible.
- Configure the Azure Defender for SQL . It includes Advanced Threat Detection, vulnerability assessments, and data discovery and classification capabilities.
- Use Advanced Threat Protection for Azure SQL Database to detect Denial of Service (DoS) attacks against databases. It also detects other harmful attempts to access or exploit databases like SQL injection attacks, Credentials theft/leak, Privilege abuse, Data exfiltration, etc.
- Set up escalation alerts for critical situations. Advanced threat protection provides security alerts on anomalous activities. These alerts help ensure that security teams are aware of issues as soon as they occur and can prevent incidents from being overlooked.
- Set up Azure networking components using the Microsoft best practices.
Audit your databases periodically
Auditing helps you monitor unauthorized activities, vulnerabilities in access permissions or configurations, and maintain regulatory compliance. The specific audits you should enable depends on your data use and what compliance standards apply to your data.
- Auditing tracks database events and writes them to an Audit log/ Activity log in your Azure storage account. When saving Audit logs to Azure Storage, ensure that access to the Storage Account is restricted to the minimal security principles. Control who has access to the storage account.
- Track Azure Database health using Azure monitor activity logs.
- Use threat detection to detect anomalous database activities indicating potential security threats to the database.
- Use data encryption to avoid information leakage to the Auditor when auditing access to sensitive data. For more information, see the article Protect sensitive data in use from high-privileged, unauthorized users.
Ensure that the databases are configured to meet security best practices
Enable SQL Vulnerability Assessment (VA) to scan your database for security issues periodically automatically.
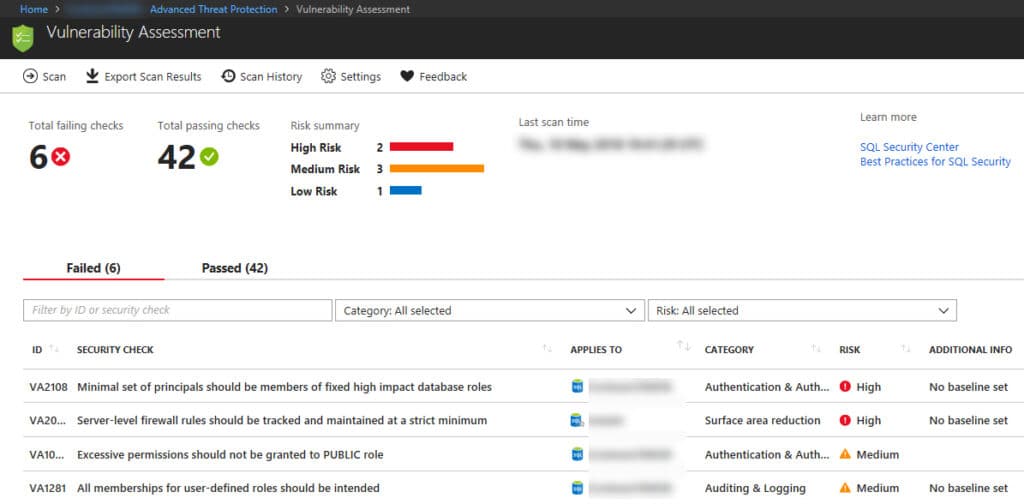
It can help you identify misconfigurations, unprotected data, and excessive permissions at database and server levels.
For any vulnerabilities found, evaluate the drift from the previous scan result and determine if the check should be resolved.
Is your company ready to implement the Azure SQL Securities?
Azure provides many built-in security features, but not all of the security features are automatic. In fact, many require configuration, and not all requirements apply to all environments.
Remember that Azure SQL is a dynamic platform. Be sure to keep abreast of new changes and apply necessary security adjustments continually—the more current your security operation, the better your posture.